Если нужно создать удаленное подключение для нескольких пользователей, то сперва необходимо настроить терминальный сервер на Windows Server. Он позволит предоставлять ровно такое количество мощностей, которое требуется для решения конкретной задачи – например, для работы с 1С или CRM.
Настройка в версиях Windows Server 2012, 2016, 2019 выполняется по одному алгоритму.
- Базовая настройка терминального сервера
- Добавление ролей и компонентов
- Настройка конфигурации развертывания
- Настройка зоны обратного просмотра
- Настройка DHCP
- Установка служб удаленных рабочих столов
- Настройка лицензирования удаленных рабочих столов Windows
- Добавление лицензий
- Предварительные условия
- Установка базовых ролей службы удаленных рабочих столов
- Пошаговая установка
- Добавление дополнительного сервера
- Добавление роли RD Gateway Role
- Настройка параметров установки
- Верификация службы удаленных рабочих столов
- Installation of Remote Desktop Services base roles
- Add secondary server
- Add RD Gateway Role
- Configure deployment properties
- Eliminate Data Loss Eliminate Ransomware
- Настройка RDP на Windows Server 2019
- What is Hyper-V Server 2019?
- Hyper-V host settings
- Virtual Machines
- Virtual Switches
- Checkpoints
- VMConnect and Remote Management
- Viewing Hyper-V Event Logs
- Wrapping Up
- Windows Server 2019 ReFS and Deduplication
- Storage Spaces Direct Improvements
- Windows Admin Center
- Shielded VM improvements
- Encrypted Subnets
- Simplified Two-Node Clusters
- Takeaways
Базовая настройка терминального сервера
Сначала проверим имя рабочей группы и описание компьютера.
- Открываем «Панель управления», переходим в раздел «Система».
- Нажимаем «Изменить параметры».
- На вкладке «Имя компьютера» смотрим, как он идентифицируется в сети. Если имя компьютера или рабочей группы слишком сложное, нажимаем «Изменить» и задаем другие идентификаторы. Для применения нужно перезагрузить систему.
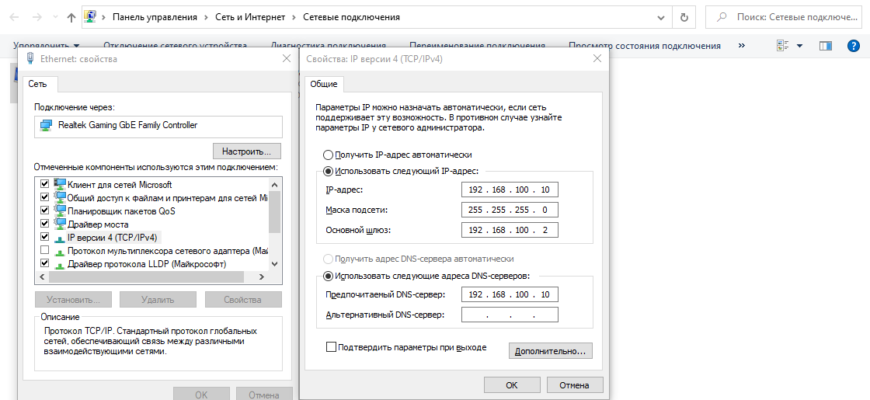
После проверки имени смотрим и при необходимости меняем сетевые настройки. В «Панели управления» открываем раздел «Сетевые подключения».
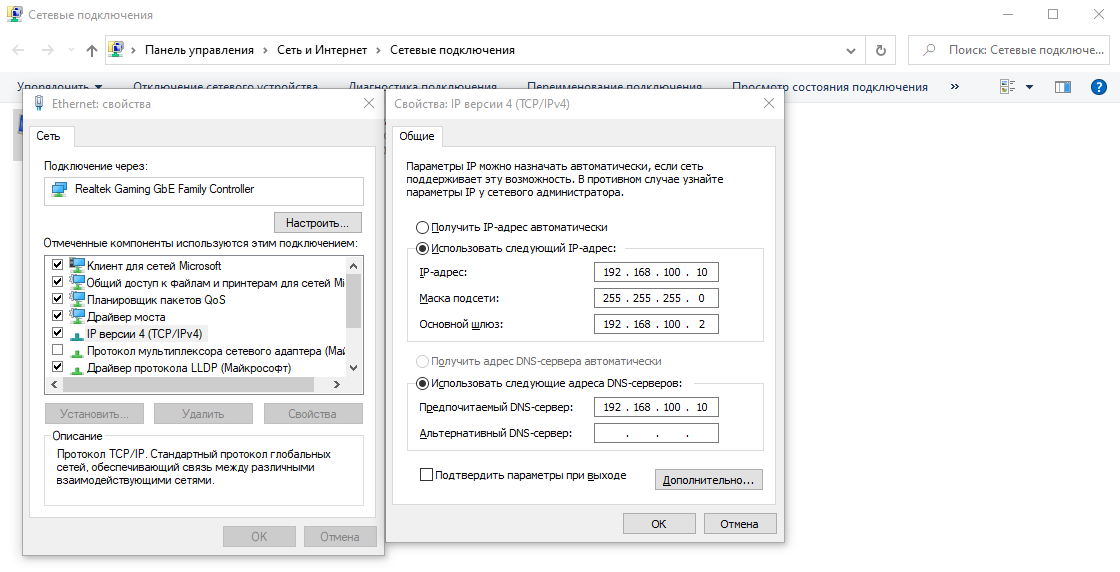
Переходим в свойства используемого подключения, открываем свойства «IP версии 4». Указываем настройки своей сети. IP, маска и шлюз должны быть статичными.
Комьюнити теперь в Телеграм
Подпишитесь и будьте в курсе последних IT-новостей
Подписаться
Добавление ролей и компонентов
Открываем меню «Пуск» и запускаем «Диспетчер серверов». Далее:
- Нажимаем «Добавить роли и компоненты».
- Выбираем пункт «Установка ролей или компонентов».
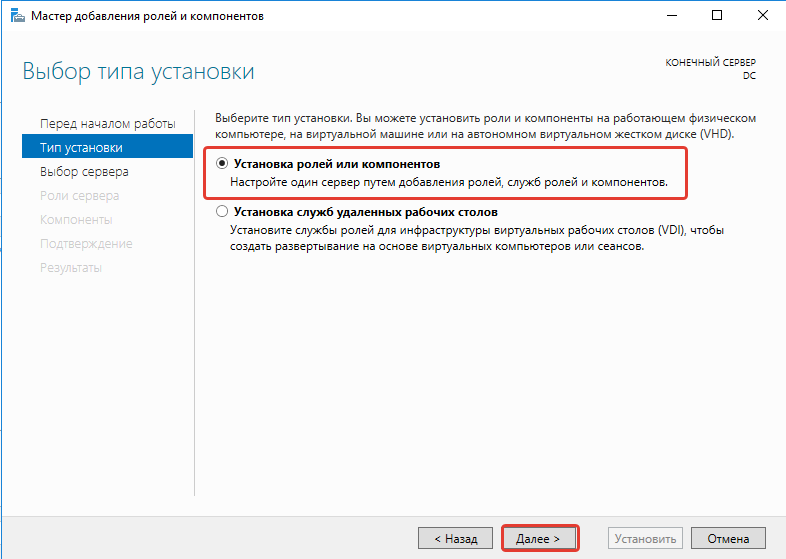
- Выбираем сервер из пула серверов.
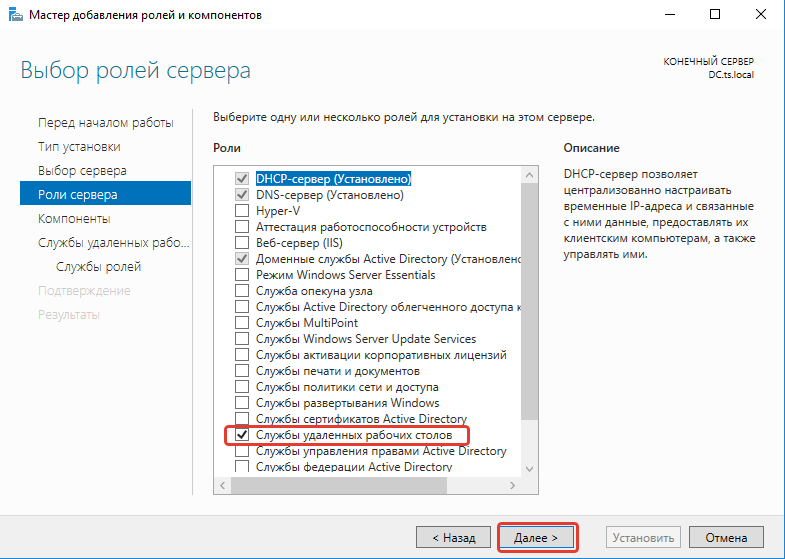
- В разделе «Роли сервера» отмечаем DHCP-сервер, DNS-сервер, доменные службы Active Directory, службы удаленных рабочих столов.
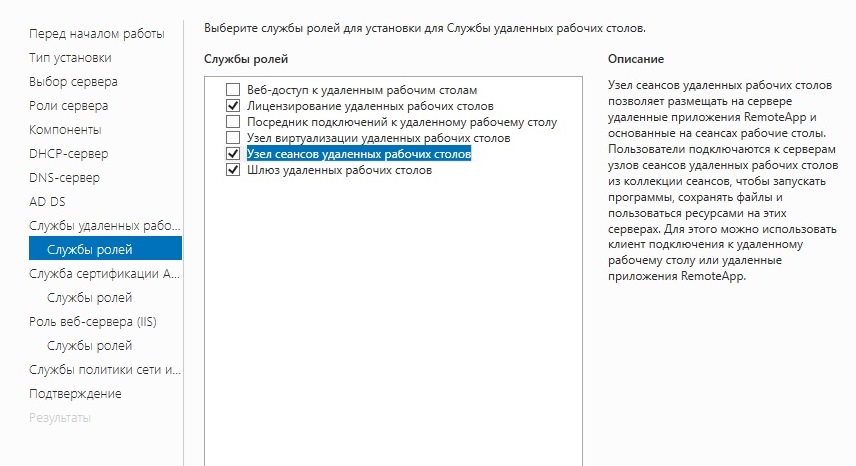
- В разделе «Службы ролей» отмечаем лицензирование удаленных рабочих столов, узел сеансов удаленных рабочих столов и шлюз удаленных рабочих столов.
- Нажимаем «Далее» до раздела «Подтверждение». Здесь нажимаем «Установить».
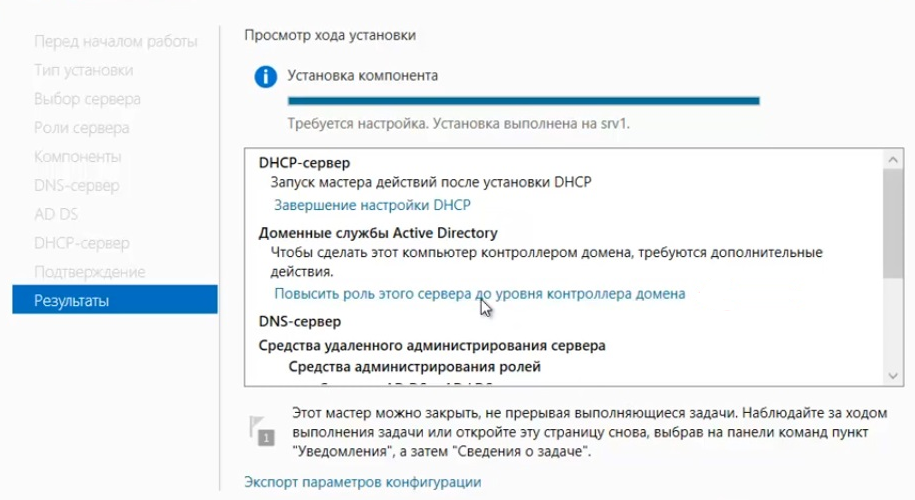
После завершения установки выбираем повышение роли этого сервера до уровня контроллера доменов.
Настройка конфигурации развертывания
Теперь нужно настроить корневой домен:
- В мастере настройки доменных служб Active Directory выбираем операцию добавления нового леса и указываем имя корневого домена. Оно может быть любым.
- В разделе «Параметры контроллера» придумываем и подтверждаем пароль.
- Проходим до раздела «Дополнительные параметры». Указываем имя NetBIOS, если его там нет.
- Проходим до раздела «Проверка предварительных требований». Если проверка готовности пройдена, нажимаем «Установить». Если нет, устраняем недостатки.
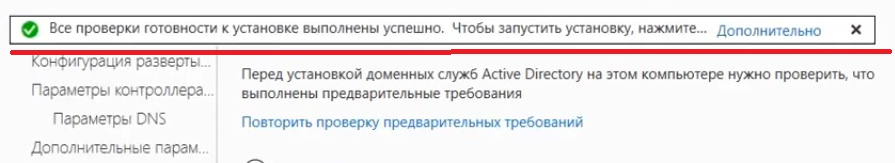
После завершения установки необходимо перезагрузиться.
Настройка зоны обратного просмотра
В «Диспетчере серверов» раскрываем список средств и выбираем DNS. Далее:
- Нажимаем «Зона обратного просмотра» – «Создать новую зону».
- Выделяем пункт «Основная зона».
- Выбираем режим «Для всех DNS-серверов, работающих на контроллере домена в этом домене».
- Выбираем зону обратного просмотра IPv4.
- Указываем идентификатор сети – часть IP адресов, которые принадлежат этой зоне.
- Нажимаем «Готово» для применения конфигурации.
Проверить, что все установилось, можно в «Диспетчере DNS».
Настройка DHCP
Возвращаемся в «Диспетчер серверов». Здесь нужно завершить настройку DHCP.
- Указываем данные для авторизации.
- Проверяем сводку и нажимаем «Закрыть».
- После завершения установки снова открываем «Диспетчер серверов» – «Средства» – DHCP.
- В окне DHCP проходим по пути «»«»«»
- Задаем любое имя DHCP.
- Выбираем настройку этих параметров сейчас.
- В окне DHCP переходим по пути «»«»«»
Установка служб удаленных рабочих столов
После настройки DHCP снова открываем «Диспетчер серверов».
- Нажимаем «Управление» – «Добавить роли и компоненты».
- Выбираем установку служб удаленных рабочих столов.
- В разделе «Тип развертывания» выбираем «Быстрый запуск».
- В разделе «Сценарий развертывания» выбираем развертывание рабочих столов на основе сеансов.
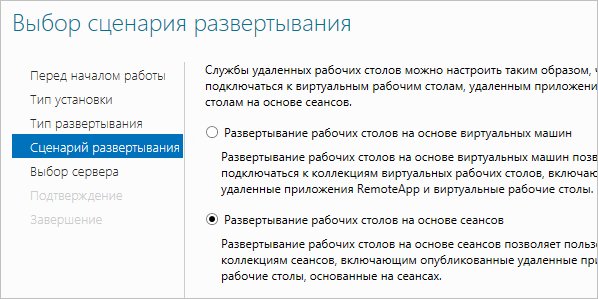
- Отмечаем пункт «Автоматически перезапускать конечный сервер, если это потребуется» и нажимаем «Развернуть».
Настройка лицензирования удаленных рабочих столов Windows
Чтобы сервер работал корректно, нужно настроить службу лицензирования.
- Открываем «Диспетчер серверов».
- Переходим по пути «Средства» – «Remote Desktop Services» – «Диспетчер лицензирования удаленных рабочих столов».
- Выбираем в списке сервер, кликаем по нему правой кнопкой и нажимаем «Активировать сервер».
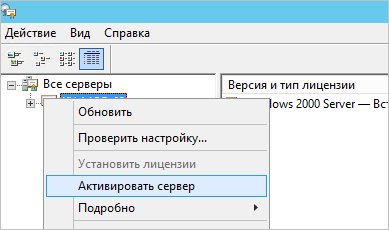
- Нажимаем «Далее» несколько раз, снимаем отметку «Запустить мастер установки лицензий» и затем – «Готово».
- Снова открываем «Диспетчер серверов».
- Переходим в «Службы удаленных рабочих столов».
- В обзоре развертывания нажимаем на меню «Задачи» и выбираем «Изменить свойства развертывания».
- Переходим в раздел «Лицензирование».
- Выбираем тип лицензии.
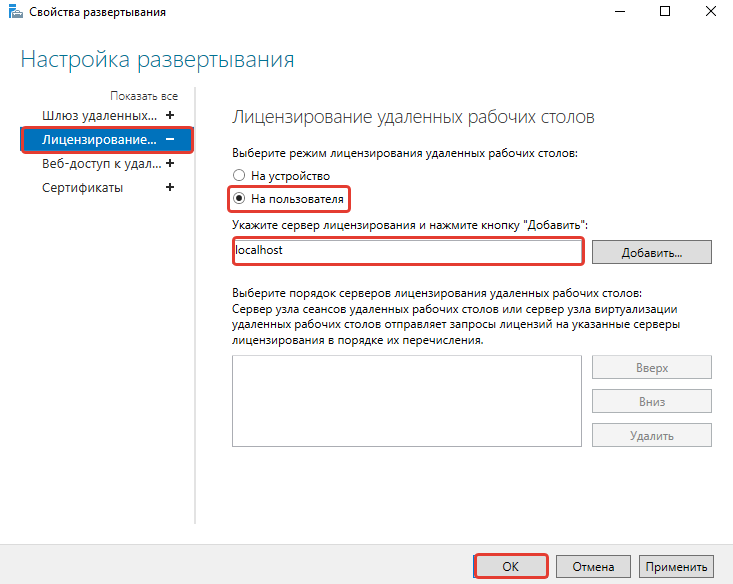
- Прописываем имя сервера лицензирования – в данном случае это локальный сервер localhost. Нажимаем «Добавить».
- Нажимаем «ОК», чтобы применить настройки.
Добавление лицензий
Осталось добавить лицензии.
- Открываем «Диспетчер серверов».
- Переходим по пути «Средства» – «Remote Desktop Services» – «Диспетчер лицензирования удаленных рабочих столов».
- Кликаем по серверу правой кнопкой и выбираем пункт «Установить лицензии».
- В мастере установки лицензий выбираем программу, по которой были куплены лицензии.
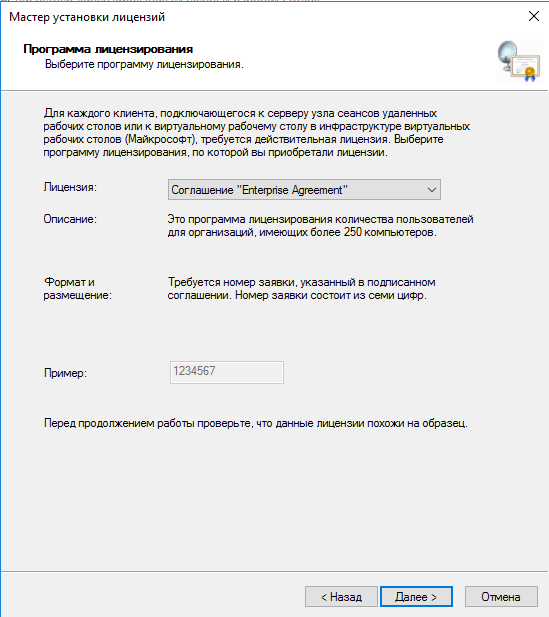
- Указываем номер соглашения и данные лицензии.
- Применяем изменения.
Чтобы проверить статус лицензирования, открываем «Средства» – «Remote Desktop Services» – «Средство диагностики лицензирования удаленных рабочих столов».
На этом настройка терминального сервера на Windows Server завершена. Теперь к серверу могут подключаться удаленные пользователи для выполнения разных задач.
Установка службы удаленных рабочих столов (RDS) на Windows Server 2019 состоит из многих шагов, но в действительности это очень просто. Из статьи вы узнаете о том, как установить эту службу в доменной среде, которая требует наличия двух серверов.
Предварительные условия
Перед началом установки RDS необходимо убедиться, что выполняются два требования, а именно:
- все серверы подключены к домену;
- есть по крайней мере два доступных сервера.
Необходимо, чтобы было именно два сервера, так как для роли RD Licensing, согласно лучшим практикам Microsoft, требуется отдельный сервер. В данной инструкции мы будем использовать для этой роли контроллер домена, что не вполне соответствует лучшим практикам, но мы делаем это, чтобы упростить демонстрационную установку.
Установка базовых ролей службы удаленных рабочих столов
Для начала мы добавим к основному RDS-серверу следующие роли:
- RD Connection Broker (Посредник подключений к удаленному рабочему столу);
- RD Web Access (Веб-доступ к удаленным рабочим столам);
- RD Session Host (Узел сеансов удаленных рабочих столов).
Пошаговая установка
- В диспетчере сервера на основном RDS-сервере, на котором выполняется установка, откройте Add Roles and Features Wizard (мастер добавления ролей и компонентов) и выберите Remote Desktop Services installation(установку службы удаленных рабочих столов).

2. Для этой инструкции мы используем опцию Quick Start (Быстрый старт), но если вам требуется больше контроля над процессом установки, вы можете выбрать Standard Deployment (Стандартную установку), которая позволяет редактировать большее количество настроек.

3. Далее мы выбираем Session-based desktop deployment (Установка рабочих столов на основе сеансов), так как это стандартная модель подключения к удаленным приложениям и удаленным рабочим столам, используемая в большинстве установок RDS.

4. В разделе Server Selection (Выбор сервера), выберите сервер, на который мы устанавливаем RDS.

5. Чтобы начать установку, выберите Restart the destination server automatically if required (Автоматический перезапуск конечного сервера в случае необходимости) и кликните на Deploy (Установить).

6. Проверьте, что все роли успешно установлены перед тем, как переходить к следующим шагам.

Добавление дополнительного сервера
В этой инструкции мы используем доменный контроллер в качестве сервера лицензирования удаленных рабочих столов, но для упрощения установки этой роли мы можем добавить дополнительный сервер в диспетчере серверов.
- Чтобы добавить дополнительный сервер, кликните правой кнопкой мыши на All Servers (Все серверы), выберите Add Servers (Добавление серверов), а затем выберите нужный сервер в Active Directory.
2. Перейдите на экран Remote Desktop Services (Службы удаленных рабочих столов) и кликните на зеленом плюсе над RD Licensing (Лицензирование удаленных рабочих столов).

3. Откроется окно Add RD Licensing Servers (Добавление серверов лицензирования удаленных рабочих столов), в котором вы сможете выбрать дополнительный сервер для роли RD Licensing.

4. Кликните на Add (Добавление), чтобы установить роль на дополнительный сервер.

5. Убедитесь, что установка завершена и зеленый плюс над RD Licensing заменен на соответствующий значок.

Добавление роли RD Gateway Role
Теперь нам нужно добавить RD Gateway Role (роль службы шлюза удаленных рабочих столов) к основному RDS-серверу.
- На экране Remote Desktop Services (Службы удаленных рабочих столов) кликните на зеленом плюсе над RD Gateway (Шлюз удаленных рабочих столов).
- Выберите основной RDS-сервер для установки этой роли.

3. Присвойте самоподписанному SSL-сертификату полное доменное имя.
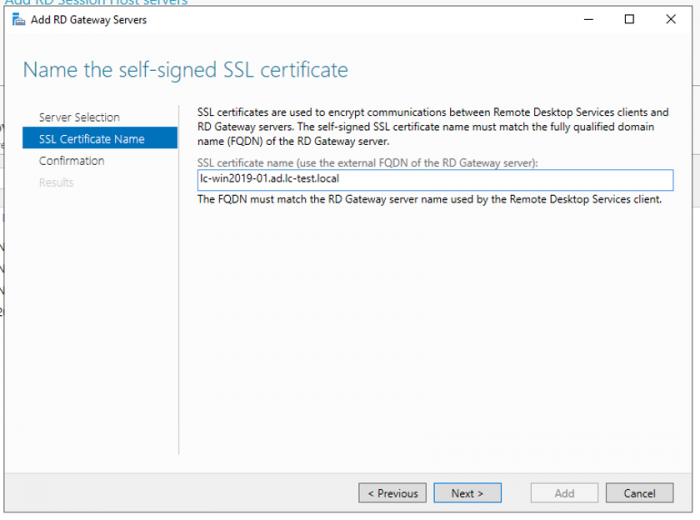
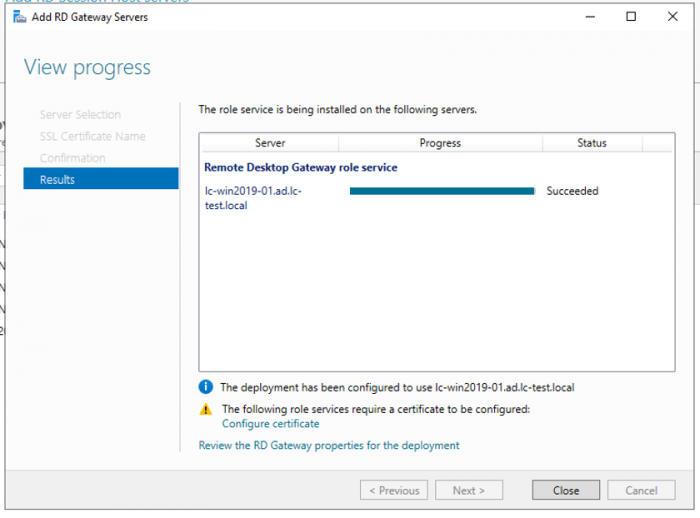
4. Кликните Next и потом Add, чтобы установить роль на основной RDS-сервер.
Настройка параметров установки
Теперь, когда все роли установлены, можно перейти к настройке параметров установки.
- Откройте экран Remote Desktop Services и в выпадающем списке Tasks (Задания) кликните на Edit Deployment Properties (Редактирование параметров установки).

2. На экране RD Gateway оставьте настройки по умолчанию и кликните на пункте меню RD Licensing.

3. Выберите Per User (По количеству пользователей) на экране RD Licensing. Вы можете выбрать любую из двух опций, но в целях обучения мы выбираем Per User.

4. Обратите внимание на URL на экране RD Web Access (Веб-доступ к удаленным рабочим столам). Позже мы будем его использовать для доступа к установленным приложениям.

5. В целях тестирования можно оставить сертификаты как Not Configured (Не сконфигурированные) и нажать OK, чтобы сохранить параметры установки.

Если вы хотите сконфигурировать сертификат, вам придется делать это для каждой службы роли по отдельности.
Верификация службы удаленных рабочих столов
По умолчанию после установки создается QuickSessionCollection, куда входят Calculator, WordPad и Paint в качестве удаленных приложений. Мы можем использовать это для тестирования установки RDP.
- Для тестирования IIS перейдите по ссылке, представленной на экране RD Web Access, или используйте https://localhost/rdweb/, если вы находитесь на RDP-сервере.

2. Подключитесь к сеансу IIS RDS с помощью доменной учетной записи.

3. Запустите удаленное соединение: то, которое вы сконфигурировали, или удаленное приложение по умолчанию.

Установка службы удаленных рабочих столов может состоять из многих шагов, но после изначальной настройки ее легко конфигурировать и использовать. Удаленные приложения обеспечивают значительную гибкость, как и возможность настраивать коллекции RDP-подключений для предложения их пользователям.
Installing Remote Desktop Services (RDS) on Windows Server 2019 appears to take many steps, but in reality is quite easy. In this article, we dive into how to install these services in a domain environment that requires two servers.
There are only two necessary steps before we embark on installing RDS. Those are:
- All servers are domain joined
- There are at least two available servers
The reason that we need two servers is that the RD Licensing role will go on the second server rather than all on one, as this is considered a Microsoft best practice. In this tutorial, we use the Domain Controller as the RD License server which would not be considered best practice. The reason for doing this in this tutorial is to keep the installation simple.
Installation of Remote Desktop Services base roles
- RD Connection Broker
- RD Web Access
- RD Session Host
- Within Server Manager on the primary RDS server that we are installing, open the Add Roles and Features Wizardand select Remote Desktop Services installation.
2. For this tutorial we are going to choose Quick Start, but if you need further control over the installation process, you can use the Standard Deployment to modify more options during installation.
3. Next, we will choose Session-based desktop deployment, as this is a common RemoteApp and desktop session model that is commonly used in more traditional RDS deployments.
4. In the Server Selection, choose the server where we are installing RDS.
5. Choose Restart the destination server automatically if required and click on Deploy to start the installation.
6. Verify that all roles have succeeded in installation before moving on to the next steps.
Add secondary server
For this tutorial, we are going to use the Domain Server as our RD Licensing server, but to easily install that role, we can add an additional server to the Server Manager.
- Add the secondary server by right-clicking on the All Servers, choosing Add Servers, and then picking the server from Active Directory.
2. Navigate to Remote Desktop Services and click on the green plus for RD Licensing.
3. The Add RD Licensing Servers screen will appear and that will let you add the secondary server as a target for the RD Licensing role.
4. Click on Add to install the role on the secondary server.
5. Verify that the installation is complete by seeing the green plus replaced by the proper icon in RD Licensing.
Add RD Gateway Role
Finally, we need to add the RD Gateway Role to our primary RDS server.
- Under the Remote Desktop Services screen, click on the green plus over RD Gateway.
- Select the primary RDS server to use for the installation of this role.
3. Name the self-signed SSL certificate with a Fully-Qualified Domain Name.
4. Click on Next and then Add to install the role to our primary RDS server.
Configure deployment properties
Now that all the roles have been installed, we can configure the actual deployment properties.
- Navigate to the Remote Desktop Services screen and under the Tasks dropdown, click on Edit Deployment Properties.
2. Leave the default settings on the RD Gateway screen and click on the RD Licensing menu item.
4. Note the URL of the RD Web Access screen as this will be used later to access the applications deployed.
5. For the purposes of testing, you can leave the certificates Not Configured, and finally click on OK to save the deployment configuration.
If you do want to configure a certificate, you will have to do this for each and every role service individually
By default, a QuickSessionCollection was created upon installation that contains Calculator, WordPad, and Paint as RemoteApps. This can be used to test the RDP deployment.
- Navigate to the IIS URL originally located in RD Web Access, or you can use https://localhost/rdweb/ if you are located on the RDP server itself, to test IIS.
2. Log into the IIS RDS session using domain credentials.
3. Finally, launch a remote connection, either one you have defined or a default RemoteApp.

Adam Bertram
Adam Bertram is a 20-year veteran of IT and an experienced online business professional. He’s a consultant, Microsoft MVP, blogger, trainer, author and content marketing writer for multiple technology companies.
More about author

Cheers for trusting us with the spot in your mailbox!
Now you’re less likely to miss what’s been brewing in our blog with this weekly digest.

Eliminate Data Loss
Eliminate Ransomware
#1 Backup and Recovery

Настройка RDP на Windows Server 2019
Проверяем версию сервера Windows Server 2019, заходим в консоль, вводим winver, если сборка 1809, то выполняем две команды:
takeown /F c:\Windows\System32\termsrv.dll /A
icacls c:\Windows\System32\termsrv.dll /grant Администраторы:F
И подменяем файл из вложения в папку c:\Windows\System32
Настраиваем терминальный сервер:
Через диспечер сервера устаналиваем компоненты:
Служба удаленных рабочих столов, далее — Лицензирование сервера терминалов
Перезагружаемся
Ищем в меню «Диспечер лицензирования удаленных рабочих столов», открываем «Все серверы», выбираем наш сервер, правой кнопкой — Активировать
Затем через ПКМ выбираем «Установить лицензии», выбираем «другое соглашение», выбираем лицензирование на устройство, указываем номер 6565792, указываем количество пользователей.
Настраиваем групповую политику чтобы сервер видел «Сервер лицензирование сервера терминалов»:
Пуск — выполнить gpedit.msc
Конфигурация компьютера, Административные шаблоны, Компоненты Windows, Службы удаленных рабочих столов, Узел сеансов удаленных рабочих столов, Лицензирование — Использовать указанные серверы лицензирования удаленных рабочих столов:
Делаем вкл и указываем адрес 127.0.0.1
Перезагружаемся, радуемся жизни.
Если у нас сборка винды отличается от 1809, то качаем hex-редактор, копируем
И ищем в нем тексты:
| Windows 10 x64 1909 | 39 81 3C 06 00 00 0F 84 5D 61 01 00 |
| Windows 10 x64 1903 | 39 81 3C 06 00 00 0F 84 5D 61 01 00 |
| Windows 10 x64 1809 | 39 81 3C 06 00 00 0F 84 3B 2B 01 00 |
| Windows 10 x64 1803 | 8B 99 3C 06 00 00 8B B9 38 06 00 00 |
| Windows 10 x64 1709 | 39 81 3C 06 00 00 0F 84 B1 7D 02 00 |
На Windows Server 2019 1809 у меня не нашло согласно табличке, нашел то что максимально подходило.
И исправляем этот набор символов на
B8 00 01 00 00 89 81 38 06 00 00 90
После этого опять подменяем библиотеку termsrv.dll
Starting in Windows Server 2019, Microsoft has made it clear that the way forward for managing Windows Server 2019 and future Windows versions will be the new Windows Admin Center (WAC) management tool.
Windows Admin Center provides a new management dashboard that replaces the now aging Server Manager tool that is found in Windows Server 2019 and previous Windows Server releases.
Windows Admin Center now provides the ability to manage Windows Server 2019 Hyper-V as well as many other management tasks to note. What about the free Hyper-V 2019 Server?
In this post we will look at Hyper-V server 2019 Windows Admin Center management and see what features are found in Microsoft’s new administration tool for Windows Server 2019 and Hyper-V Server 2019 to manage your Hyper-V environment.
What is Hyper-V Server 2019?
In case you are not familiar with Hyper-V Server 2019, it is the free version of Hyper-V that you can download to run virtualized workloads. The hyper-V is totally free, much like VMware’s ESXi free hypervisor.
Hyper-V Server 2019 is nothing more than a special version of Windows Server Core with the Hyper-V role preinstalled. So, as soon as you install the Hyper-V Server 2019 box, you are ready to start spinning up VMs.
There are some limitations with Hyper-V Server 2019. One of the big ones is that you don’t get any licensing benefits with your Windows guest virtual machines like you do with either Windows Server 2019 Standard or Windows Server 2019 Datacenter.
However, especially if you are going to be running Linux workloads, Hyper-V Server 2019 provides a great platform to do this for free.
The question arises, what about Hyper-V Server 2019 Windows Admin Center Management? Can you use the new Microsoft tool to manage the free version of Hyper-V Server 2019? Yes you can.
One of the things that has always bugged me about Hyper-V is the myriad of tools that you need to use to really be effective as an administrator. You find that you need to use Hyper-V Manager for some things, then Failover Cluster Manager for others.
Windows Admin Center management of Hyper-V Server 2019 shows promise. With Windows Admin Center, you can manage your single host Hyper-V servers as well as Windows Server Failover Clusters running the Hyper-V role.
WAC provides a tool that helps to consolidate the tooling needed to interact with your Hyper-V environment effectively and efficiently in most cases. The nice thing about Windows Admin Center is that it is not just a Hyper-V only tool. It allows interacting with all other aspects of your Windows Server.
This includes:
- Device management
- Event Viewer
- Files
- Firewall
- Installed apps
- Networks
- Performance Monitor
- PowerShell
- Processes
- Registry
- Remote Desktop
- Roles & features
- Scheduled tasks
- Services
- Storage
- Updates
What about the Hyper-V specific tasks that can be performed within the Windows Admin Center? You can interact with the following:
- Hyper-V host settings
- Hyper-V host performance dashboard
- Virtual machines
- Hyper-V virtual machine performance
- Virtual machine settings
- Virtual switches
- Checkpoints
- Viewing Hyper-V event logs
Hyper-V host settings
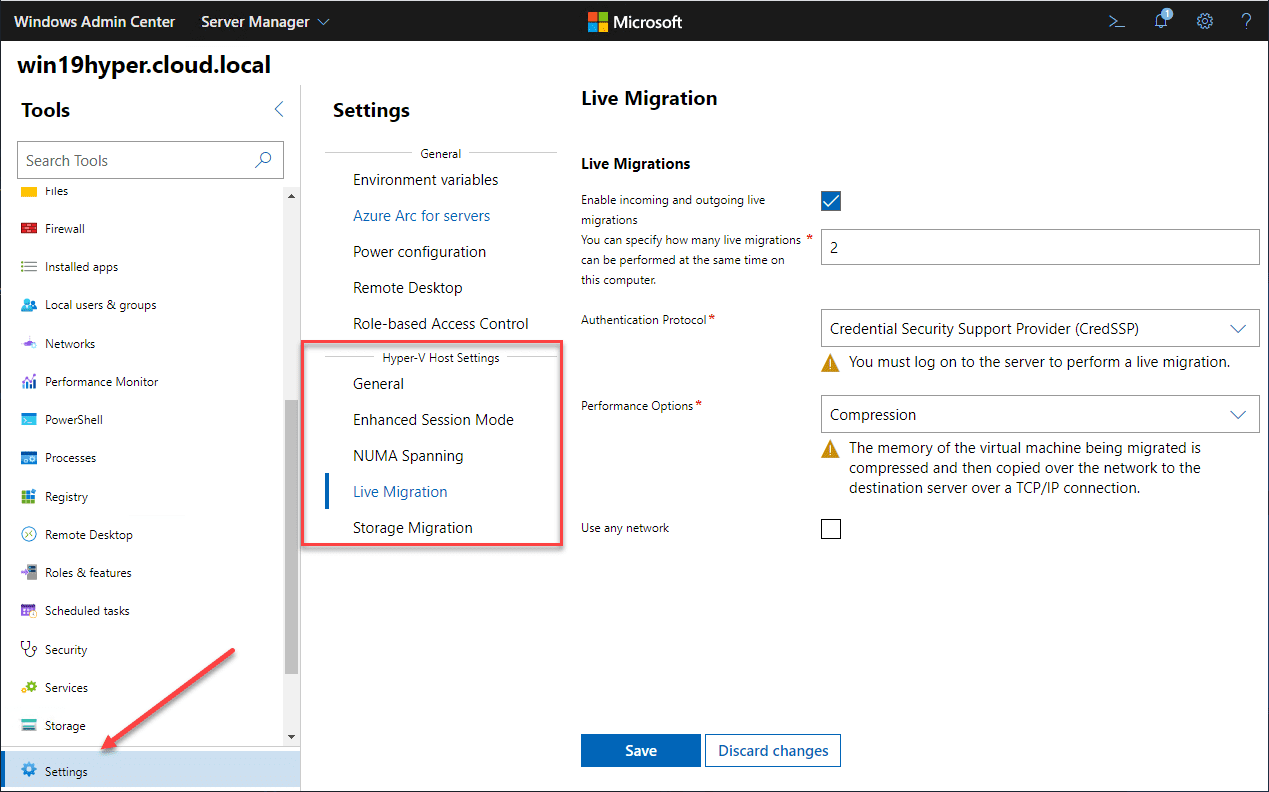
With the Hyper-V host settings, you can configure various settings related to Hyper-V on the host side of things. This includes.
- General settings
- Enhanced Session Mode
- NUMA Spanning
- Live Migration
- Storage Migration
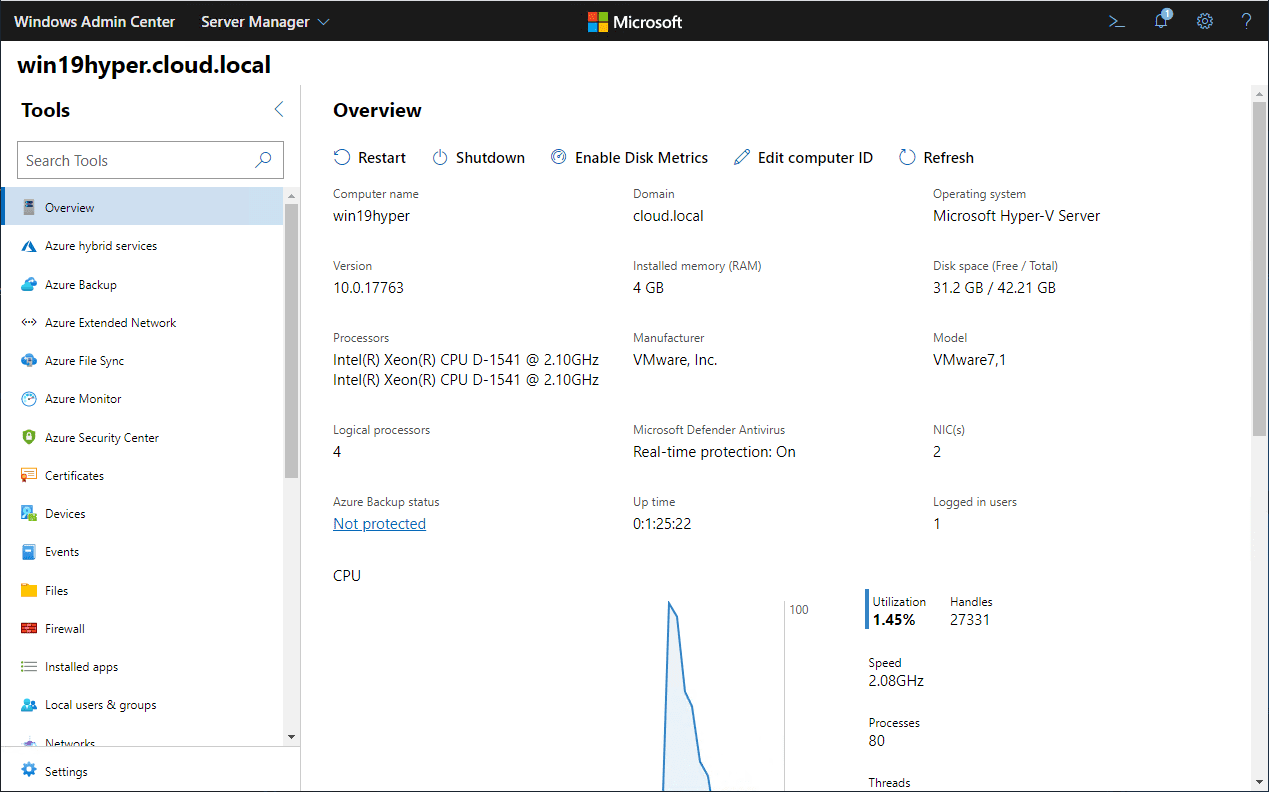
In addition, you can monitor the overall performance statistics of your Hyper-V host as well.
Virtual Machines
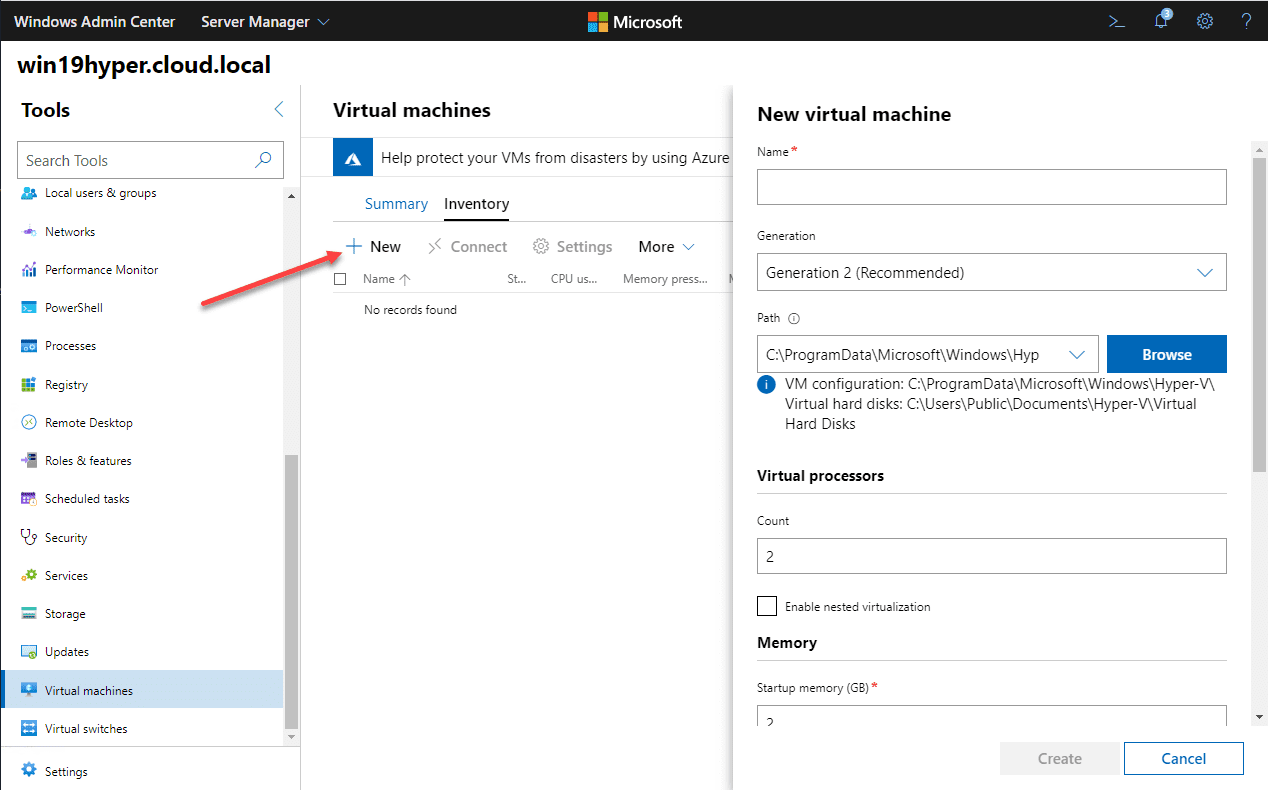
Within your Windows Admin Center connected to Hyper-V Server 2019, you can create new virtual machines. This includes all the configuration parameters that you would expect to have normally.
- Name
- Generation
- Path
- Processor and memory configuration
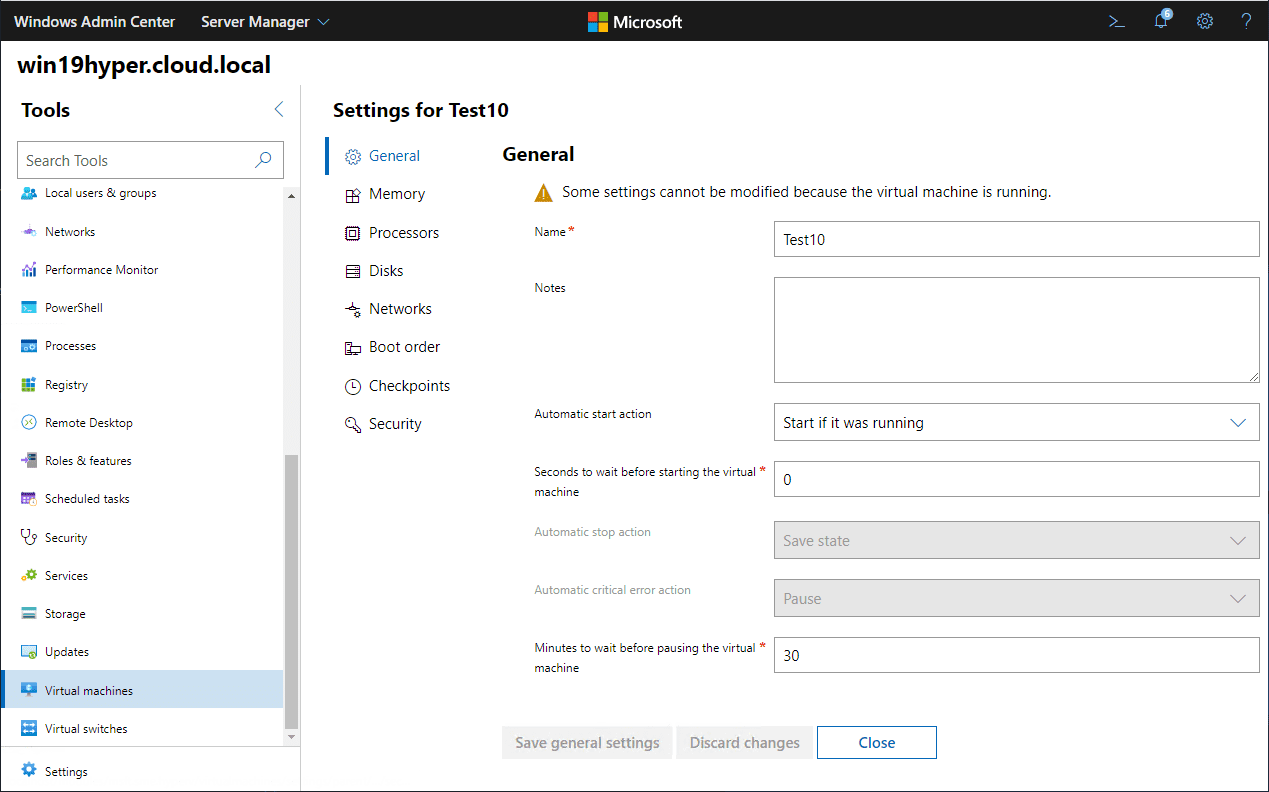
You can also dive deeper into the configuration of an existing Hyper-V Server 2019 virtual machine by clicking the virtual machine and choosing Settings.
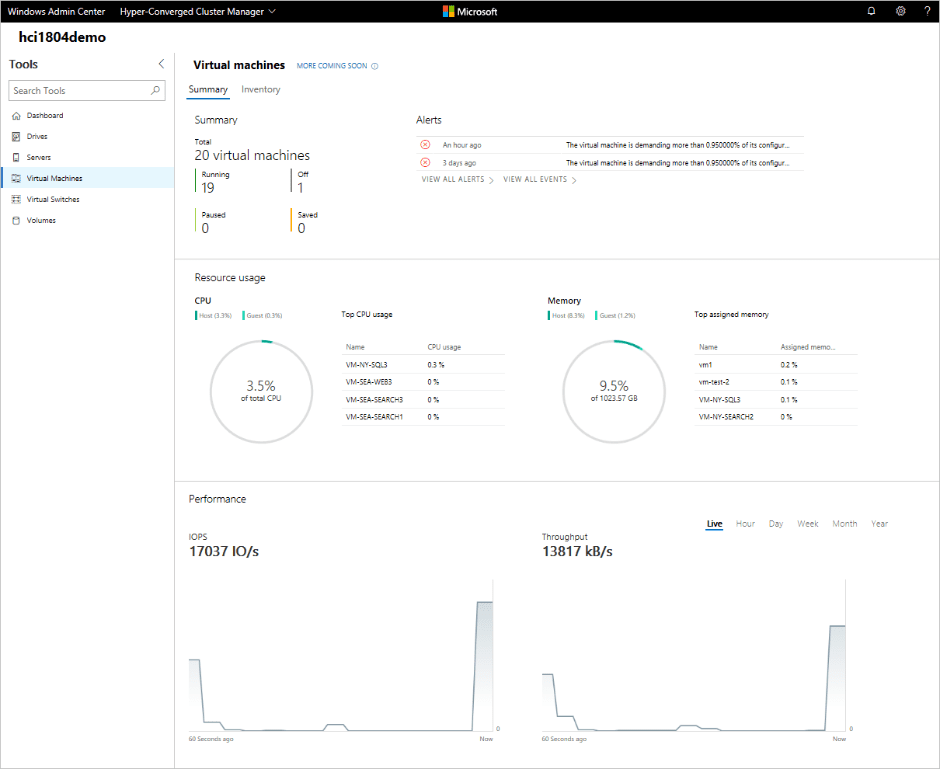
Drilling down further into the performance of the virtual machine, you have visibility by way of the virtual machine dashboard to see the general performance statistics of the virtual machine running on your Hyper-V Server 2019 host.
Virtual Switches
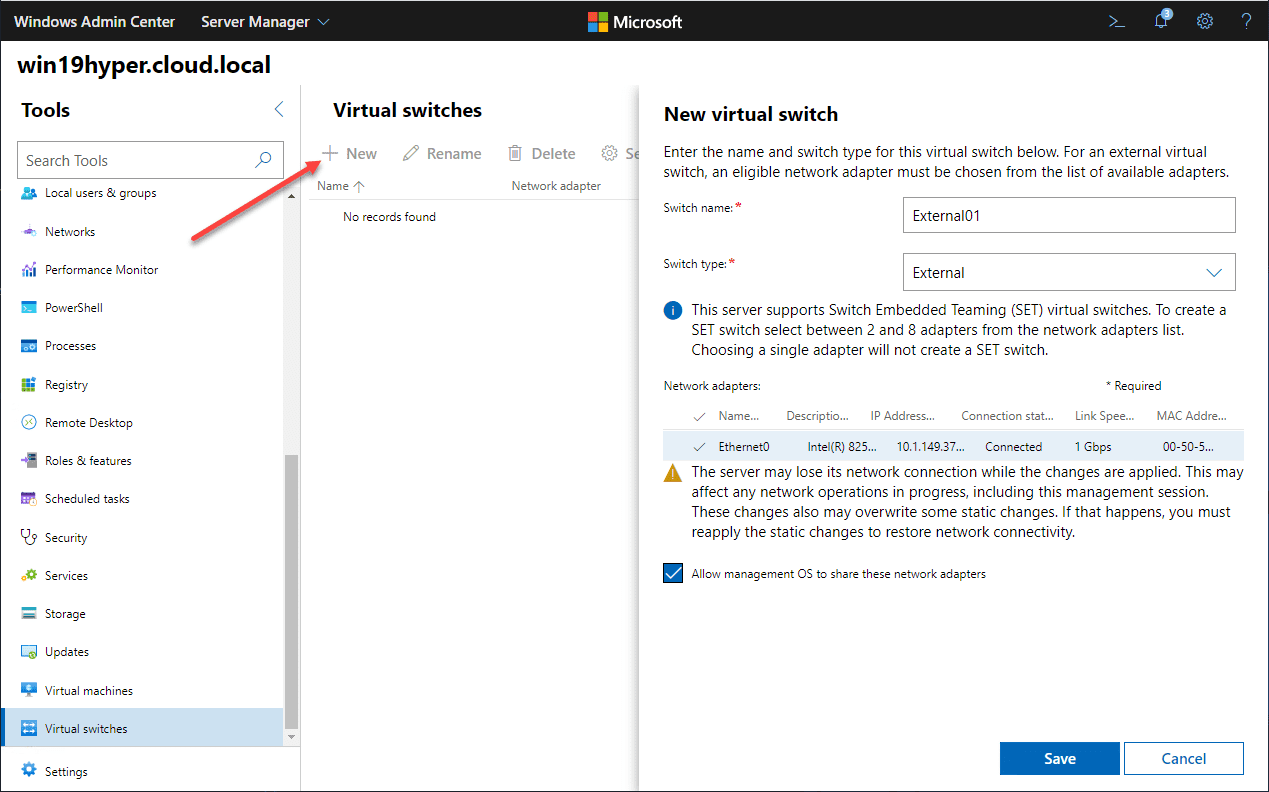
Virtual networking is a crucial aspect of your Hyper-V host and virtual machine configuration. It is nice to see that you can create the Hyper-V virtual switches in Windows Admin Center and you don’t have to fire up the trusty old Hyper-V manager to do this.
Checkpoints
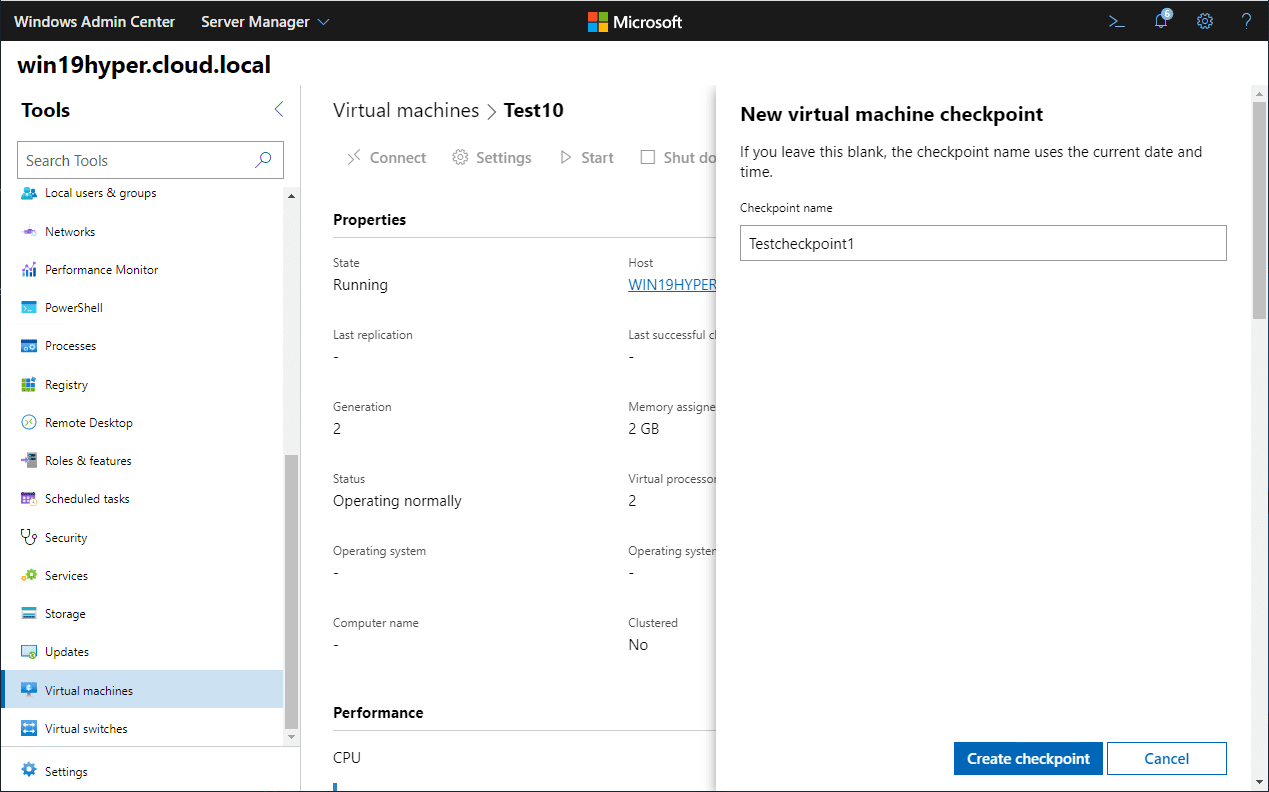
Checkpoints are also something you can create in the Windows Admin Center interface to your Hyper-V Server 2019 host.
VMConnect and Remote Management
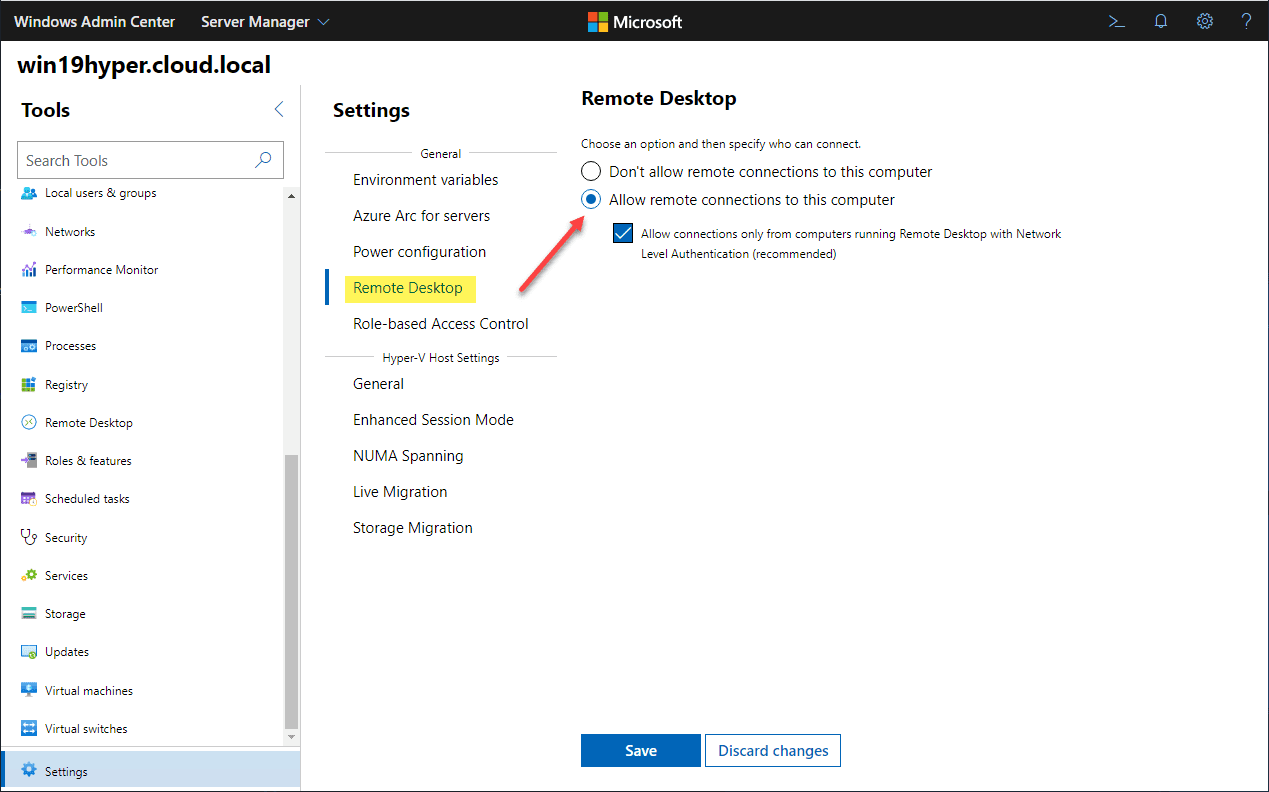
To enable the ability to connect remotely to your Hyper-V virtual machines, you need to enable remote desktop on the Hyper-V host.
Viewing Hyper-V Event Logs
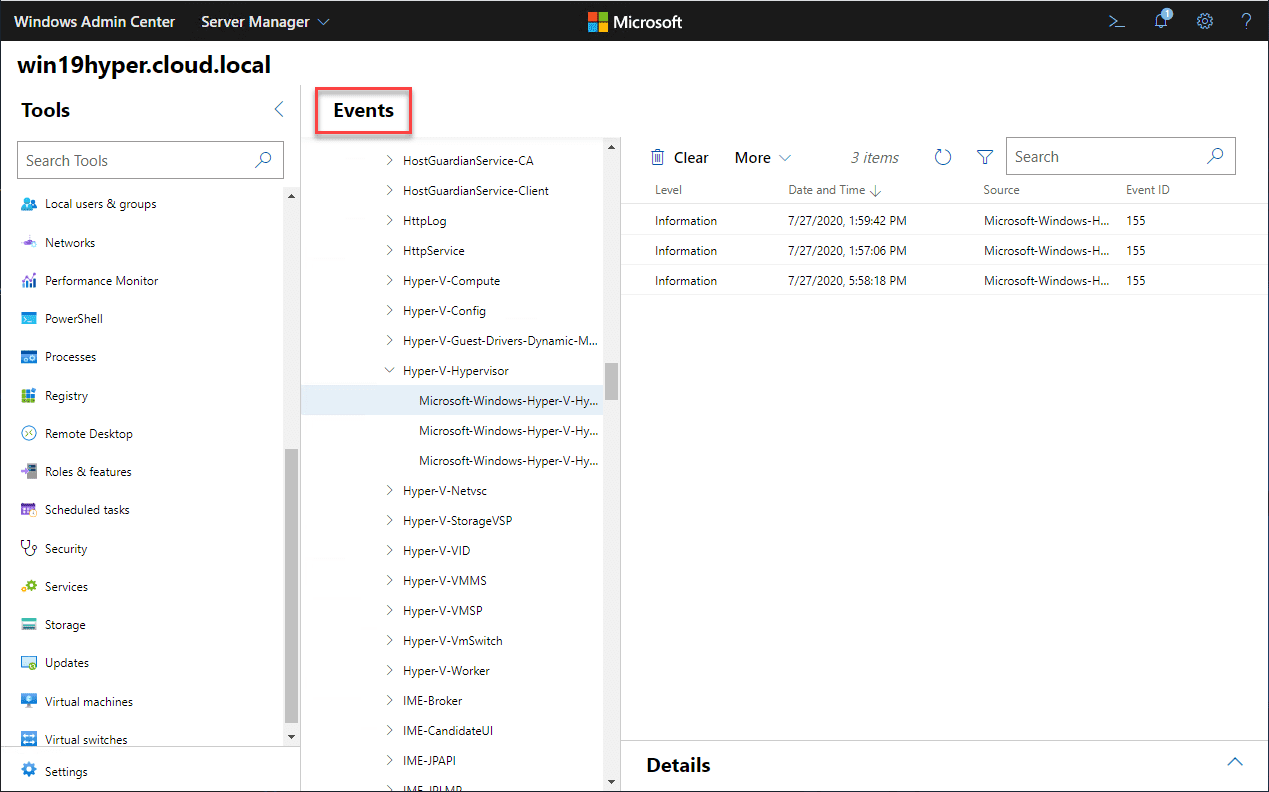
Viewing event logs is an essential part of troubleshooting any issues that may arise or to validate various Hyper-V related configuration and services. You can easily view your Hyper-V host Hyper-V logs from WAC with the Event logs module.
Wrapping Up
Hyper-V is a great virtualization platform for the enterprise datacenter that has come a long way. It can be used for traditional virtualization as well as running your hyper converged infrastructure (HCI).
Hyper-V Server 2019 Windows Admin Center Management allows you to fully make use of the free Hyper-V hypervisor while at the same time having a great management tool for the platform.
Instead of using different tools to manage the platform, Windows Admin Center allows administering your Hyper-V Server 2019 environment and all other Windows Servers you may have in the environment from a centralized management plane.
The best part about both Hyper-V Server 2019 and Windows Admin Center is they are both free for download.
- Download Windows Admin Center here
- Download Hyper-V 2019 Server here
Windows Server 2019 official download release is imminent. There were actually links that were posted over the weekend showing download links for Windows Server 2019 RTM. Windows Server 2019 as we have covered in quite a few different posts, brings a lot of new functionality and enhancements to the table. Microsoft has certainly targetted hybrid cloud as the business problem that Windows Server 2019 is more than capable of handling. Many organizations today are making use of both on-premises and public cloud infrastructure. With every Windows Server operating system release, one of the most anticipated new features that administrators are eager to get their hands on is the new capabilities found in Hyper-V. In this post, we will take a look at Windows Server 2019 Hyper-V New Features and see the new enhancements found in the latest Windows Server operating system as they relate to the Hyper-V hypervisor.
There are many new features that are found in Windows Server 2019. However, in this post, we will concentrate on the new features that relate strongly with Hyper-V. There are many new core enhancements that take Hyper-V to the next level. Let’s take a look at the following areas:
- ReFS Deduplication
- Storage Spaces Direct Improvements
- Windows Admin Center
- Shielded VM improvements
- Encrypted Subnets
- Simplified Two-Node Clusters
Windows Server 2019 ReFS and Deduplication
One of the major downsides of ReFS in Windows Server 2016 and prior was that ReFS could not be used with deduplication. Deduplication provides tremendous benefits, especially when it comes to Hyper-V since virtual machines running the same operating systems generally have a tremendous amount of duplication at the block level. With Windows Server 2019, now ReFS can be used with deduplication. This results in a tremendous amount of space savings. This helps to close the gap with using storage spaces direct and other SDS solutions on the market such as VMware vSAN that has already been able to do deduplication and compression. This will help to make ReFS an actual viable solution much more so than it has been in previous Windows Server releases.
Storage Spaces Direct Improvements
Microsoft realizes just how important software-defined storage truly is in today’s enterprise datacenter. With Windows Server 2019, a lot of development and effort has gone into improving both the performance and scale of Storage Spaces Direct. Storage Spaces Direct now supports a maximum of 4 Petabytes of storage per cluster. Additionally, Microsoft was able to show a Storage Spaces Direct cluster at Ignite that was able to post a score of 13 million IOPs for an 8 node S2D cluster. This is a great deal more performance than the Windows Server 2016 S2D cluster tested previously.
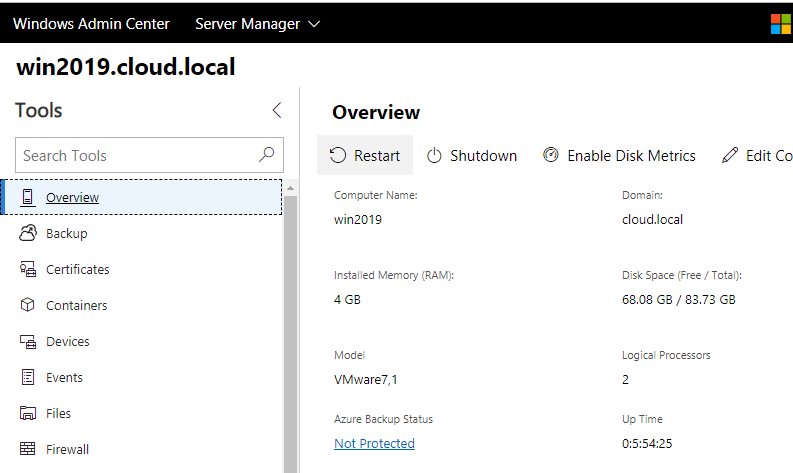
Windows Admin Center
Windows Admin center is perhaps the most highlighted single piece of software that I can remember from Microsoft in times past. Windows Admin Center is talked about just about everywhere and it is certainly a cornerstone utility for Windows Server 2019. In fact Microsoft has even written some of the Windows Server 2019 platform to be accessible only from Windows Admin Center.
As relates to Hyper-V, much more Storage Spaces Direct information is available from within the Windows Admin Center console, including a historic view of performance and health for the Storage Spaces Direct platform. Windows Admin Center also provides a centralized management plane for Hyper-V Clusters, allowing changes to be made for multiple Hyper-V hosts at the same time. Tremendous functionality is being built inside of the Windows Admin Center for Hyper-V capabilities. Third-party vendors also have the ability to extend the interface to include customized management plugins for third-party hardware and solutions.
Shielded VM improvements
Shielded VMs allow virtual machines such as domain controllers to be encrypted when they are on disk. This helps to protect against rogue administrators or attackers from gaining access to the virtual disks, taking them to another Hyper-V environment and attempting to crack passwords at their leisure. Shielded VM attestation has been improved with Windows Server 2019. The Active Directory based attestation for the host guardian service is being deprecated in favor of a host key attestation mechanism. The host key attestation mechanism provides the same basic functionality as the Active Directory based mechanism and is easier to configure.
Linux VMs are now supported for shielded VM protection. Additionally, there is a new authorized host cache that allow caching VM keys for starting up virtual machines even when the host guardian service cannot be reached. This new functionality drastically improves branch office support in making use of shielded VMs.
Encrypted Subnets
New functionality has been introduced in Microsoft’s software defined networking technology. Encrypted subnets allow administrators to specify subnets of traffic to encrypt in the software defined network infrastructure. This ensures that attackers who might have or gain physical access to the network infrastructure cannot sniff network traffic and see traffic traversing the software defined networking overlay to and from Hyper-V virtual machines.
Simplified Two-Node Clusters
Microsoft has introduced a greatly simplified architecture for Windows Server Failover Clustering technology. In Windows Server 2019, they call the technology “True Two-Node” clusters. The true two-node technology greatly simplifies the witness share that can be utilized for quorum in a two-node configuration. Traditionally, this witness node had to exist on a file server on-premises or in Azure. While not that difficult to satisfy, Microsoft has taken this even further with the true two-node configuration. With true two-node, you can use a commodity router that supports mounting a USB key in a USB port on the router. The router then allows configuring a share and permissions to the share. With true two-node you can use this share as a witness share to serve as the quorum mechanism with the two-node cluster configuration. This makes the quorum functionality for two-node extremely easy and it doesn’t require any type of Internet connectivity to work. This makes it the perfect solution for edge environments that may not have extra infrastructure to service the quorum functionality or may have sporadic connectivity or isolated connectivity.
Takeaways
Windows Server 2019 Hyper-V New Features are exciting. The new enhancements will certainly take Hyper-V to the next level for organizations making use of Hyper-V as their enterprise datacenter hypervisor of choice. Such features as ReFS with deduplication, storage spaces direct improvements, Windows Admin Center, Shield VM improvements, encrypted subnets, and simplified two-node clusters serve to make Windows Server 2019 a powerful Hyper-V platform. The download should be available any day now so administrators will be able to get their hands on the latest and greatest functionality.